2012年6月9日 星期六

Xecure Lab got security warnings for suspected state-sponsored attacks

As we all know "This site may harm your computer" warning and for years every site owner had tried hard not to get that label. Few days ago Google announced a Gmail warning message for the targets of state-sponsored attacks. Cool! How did Google do it? They can’t go into the details as those explanations would be helpful to the bad guys.
Nevertheless, at Xecure Lab, we regularly scan our personal Gmail accounts too for APT emails (our XecMail has a plugin for it) and there were no signs of APT attacks in our record recently. Surprisingly, we had chance to witness this Google state-sponsored attackers warning message:

(in English)

(in Chinese)

We speculated Google did the analysis not from "inside" by scanning the emails, e.g. looking for APT document exploit, but from "outside" by probably monitoring account login attempts involving known malicious sources or traffic protocols.

Anyway, we followed the Protect yourself now instructions, a few suggestions were given:
1. Watch out before you click a link.
2. Use a strong password.
3. Update software to the latest.
4. Enable 2-step verification.

Great, only the last one was something new at that moment, and we would like to give it a try.

With 2-step verification, Google will send SMS code to your phone when login sucessfully but with any strange device:

Oops, that means one has to repeat the above 2-step verification several times once a month, if not everyday. We also tried the "Call your phone" alternative instead of sending text, the call was from the phone number +1 (650) 353XXXX.

Lastly, when we changed the password in Google account, we'd have to go through the whole 2-step verification again. Right, a trade-off between security and convenience. ;-)

2012年6月5日 星期二

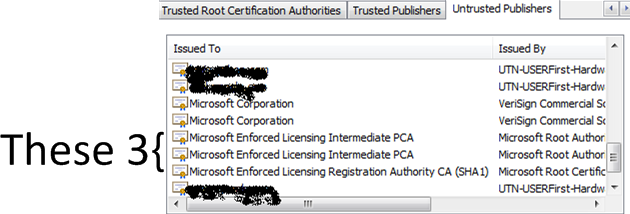
數位簽章最新用途...幫駭客蓋章!

這實在太讚了, 根據外電指出, Flame 事件中, 居然用數位簽章. 這次印章被幹走居然是偉大的微軟公司簽章...

難怪前兩天Windows Update緊急撤消了幾個簽章, 抖抖

http://www.f-secure.com/weblog/archives/00002377.html


2012年5月27日 星期日

Checkmate to Sandbox and Antivirus!


In the past few weeks, we noticed a rising number of malicious document can perfectly bypassed sandbox and all AV tools one could find on VirusTotal. Is it a zero-day exploit? No. It's simply a password-protected document. At the time of this blog, we have uploaded the sample onto VirusTotal, ThreatExpert, CWSandbox, etc, and confirmed our finding. A password-protected APT document seems like a no-brainier to beat all antivirus and sandbox on the planet.

Brandon (9bplus) also posted similar finding of these APT samples: "This document requires a password..."

Fortunately, XecScan is not bypassed. Without any update, XecScan detects them all.
The password-protected trick stops here. It is very encouraging to fans of XecScan, please continue enjoy our convenient, effective APT scanning service for free. ;-)

[ 特別通報 ] APT 惡意文件新攻擊手法 ! 擊敗所有自動化分析沙盒與掃毒軟體 !

最近這半個月來我們持續收到一些特別惡意文件,這些惡意文件有一個特色都是沙盒與掃毒軟體偵測全都是 0 !而且是完美的免殺。 上傳到VirusTotal, ThreatExpert 與 CWSandbox 全都無法分析 ! 看來駭客已經找到躲過目前所有 Anti-APT 完美方案。

9plus的 Brandon 在他的Blog(http://blog.9bplus.com)也有發現最近這些樣本

就是這麼神奇 ! XecScan在不需要更新下就可以全部捕獲,沒有誤判漏報 !
http://scan.xecure-lab.com

2012年5月25日 星期五

韓國資安業者報導: 台灣政府單位遭到 APT 攻擊 (關韓國人甚麼事? 奇怪ㄟ你)

雖然這不是新聞了, 但是在國外資安業者網站看到對我們的報導,還是關注了一下,結果我國政府機關的資安事件在韓國資安業者的網站被當 APT 宣傳材料,這...


在國外資安公司通報中看到繁體中文的個案並不多見,此例是國外業者透過 VirusTotal 比較不為人知的樣本交換加值服務方式取得,韓國資安業者刻意貼出台灣政府機關被 APT,來凸顯此問題的嚴重性,但說真的,關他們甚麼事...

從這報告的諸多信件畫面,一般社會大眾可以略窺台灣如何惡意文件滿天飛(這邊不是指言語文字上的惡意,而是開啟那個文件就會發生駭客木馬歡迎光臨的慘事),全民都應該要小心,政治人物更是要提高警覺...

工商時間: 這些 APT 不用外國人,台灣就有自主能量可以分析搞定,XecScan (http://scan.xecure-lab.com) 把 APT 通通揪出來 ;-)

2012年5月21日 星期一

Malicious PDF used in APT attacks exploiting new variants of CVE-2012-0754

Xecure Lab has discovered a new CVE-2012-0754 Flash player exploit variant being used in recent APT activities. The earliest version came from a Word document named "Iran's Oil and Nuclear Situation.doc" (see Mila's blog), where the embedded Flash codes would download an MP4 file from a remote server that contains the actual exploit codes for triggering the Flash bug. Today, the new variant we found is a malicious PDF and the MP4 is self-contained in the PDF!

2012年5月10日 星期四

Hacker's Paradise and Miserable Infosecurity (駭客天堂和資安慘業)

Though Taiwan is a tiny country with very limited natural resources, "fortunately" we have lots of cyber warfare resources to be explored. Most Taiwanese are very familiar with all sorts of scam, ranging from phone call informing your kids had been kidnapped, got a car accident, your bank account had been suspended, to your online transaction was mis-processed, or you're involved with money laundry. Yet, not many people are aware how advanced threats are endangering our daily life, business operations, critical infrastructures. Only few see it as a matter of national security.

This year, we had accepted talk invitation from a few local universities and media to share our security viewpoints with young people. Hopefully it would inspire some of them in devoting themselves to explore the information security domain.

Recording of APT attack demo (conducted in Chinese): APT Attack Demo (APT攻擊實戰)
Slides of our talk at school campus (also in Chinese though): Hacker's Paradise and Miserable Infosecurity